SANDEEP
V
Cybersecurity researcher by trade.
RF enthusiast by hobby.
Understand the system.
Question the assumptions.
I'm Sandeep V, a cybersecurity professional, red-team practitioner, penetration tester, and security researcher. I'm passionate about hands-on research and practical assessments that identify and mitigate vulnerabilities in critical systems and emerging technologies.
My work focuses on network infrastructure, IoT devices, and web applications, alongside assessments across mobile, API, cloud, thick-client, and communication systems. My current research interests include RF security, aviation security, telecom security, aircraft communications, and AI-enabled tracking systems.
I focus on reproducible observations, clear reporting, and responsible research. Through THECIDSEC, I share field guides and experiments that make complex security ideas approachable.
Professional experience.
Cyber Security Professional
Siemens / Chennai, India
- Penetration testing across web, API, mobile, thick-client, cloud, network, and communication systems.
- End-to-end vulnerability assessments across multiple platforms with actionable remediation recommendations.
- Building and using custom test automation to streamline assessments and improve detection.
- Continuing research into new attack vectors and security trends to improve testing methodologies and defensive strategies.
Technology Consultant - Security & Privacy
Protiviti India Member Pvt Ltd / Chennai, India
- Web/mobile VAPT and black-box red-team assessments of enterprise networks and server infrastructure.
- Assessment work with Burp Suite, Nessus, Nmap, Metasploit, JADX GUI, Objection, and other open-source tools.
- Malware analysis and threat-intelligence operations.
- Technical security baselines and procedures for physical and logical security.
- Microsoft Office 365 security configuration and security-policy implementation.
- Work with NIST SP 800-53, NIST SP 800-207 / zero-trust architecture, and CIS Controls v8.
SOC Analyst Intern
Cyberfort DigiSec / Chennai, India
- Real-time log monitoring with Splunk and IBM QRadar during an academic internship.
- Phishing-email and malware analysis.
- Threat-intelligence gathering and analysis.
- Emergency incident-response activities.
- Hands-on SOC operations and security monitoring.
Skills, tools, and practice.
Penetration testing
- Web application & API testing
- Network penetration testing
- Mobile application testing
- Thick-client penetration testing
- Wireless communication analysis
Security tools
- Burp Suite
- Metasploit
- Frida & Objection
- Wireshark
- Nmap & Nessus
- JADX GUI
- Other open-source penetration-testing tools
RF & aviation security
- Software-defined radio
- ADS-B analysis
- RF signal analysis
- Aviation protocol security
- Wireless security assessment
- HackRF
Network infrastructure
- Network security assessment
- Active Directory security
- Infrastructure hardening
- IoT security testing
- Network architecture review
Frameworks & standards
- NIST SP 800-53
- NIST SP 800-207 / zero-trust architecture
- CIS Controls v8
- Security baselines
- Compliance assessment
Programming & scripting
- Python
- PowerShell
- Bash scripting
- SQL
- Automation scripts
Research interests
- Red-team assessment
- Bug bounty hunting
- Network infrastructure security
- Mobile & web penetration testing
- RF security research
- Aviation security & aircraft communications
- IoT security research
- Telecom security
- AI security assessment & AI-enabled tracking systems
Research and community.
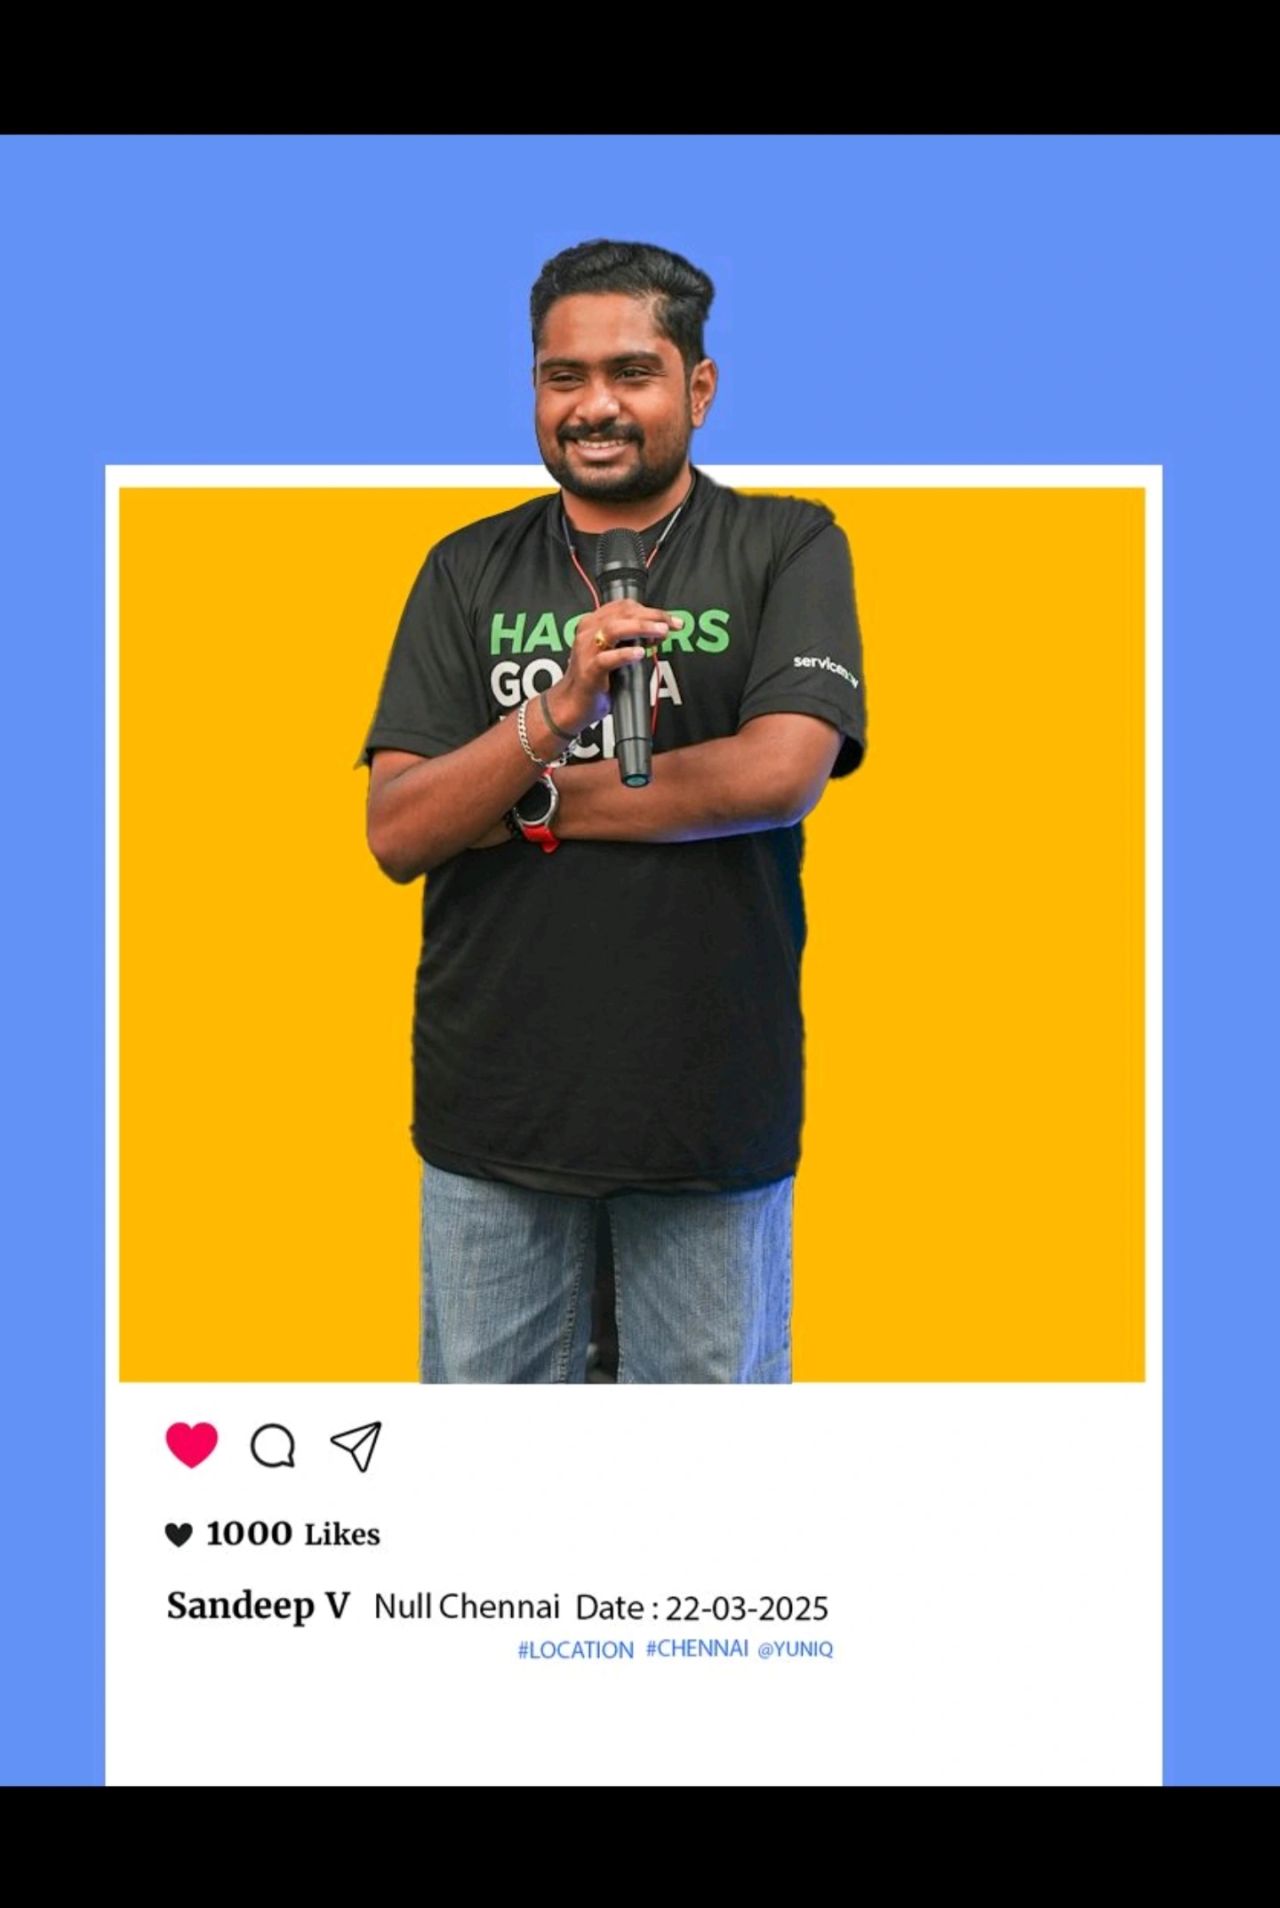
Crafting a Ghost: ADS-B Injection - The Silent Weak Link
A community presentation examining Automatic Dependent Surveillance-Broadcast (ADS-B) trust assumptions and unauthenticated broadcast data. The research connects software-defined radio, aviation communications, and the evidence needed to make a defensible security claim.
- Audience
- 100+ attendees
- Presentation
- 45 minutes
- Discussion
- Q&A session
Presentation topics
- Authentication and confidentiality limits in standard ADS-B transmissions.
- Passive reconnaissance and signal analysis using widely available SDR tools.
- Spoofed messages, injected data, and ghost-aircraft simulations as security research topics.
- Potential effects of false information on receiver and controller views.
- Aircraft movement analysis and real-time tracking.
Future research directions
- Enhanced authentication approaches for ADS-B.
- Real-time anomaly-detection systems.
- Secure communication frameworks for aviation.
Sharing the work with cybersecurity professionals, researchers, and students supports knowledge exchange and collaboration around critical-infrastructure security.
RF and aviation experiments must remain within lawful authorization and appropriate isolation. A discussion of protocol weaknesses is not permission to interfere with operational services.
Academic project: Security Procedures for Aviation Technology
Designed security procedures and practices to mitigate threats affecting aircraft, radar, air-traffic control, and airport systems.
Aviation security / radar security / ATC security / airport security.
Credentials and education.
Web Penetration Tester eXtreme (eWPTX v2)
INEProfessional certification / Penetration testing
Advanced web application penetration testing, complex attack scenarios, and advanced exploitation techniques.
Certified Ethical Hacker (CEH) Practical
EC-CouncilProfessional certification / Penetration testing
Hands-on ethical hacking and practical penetration-testing skills.
Junior Penetration Tester v2 (eJPT v2)
INEProfessional certification / Penetration testing
Penetration-testing fundamentals covering network and web application security.
Certified AppSec Practitioner (CAP)
The SecOps GroupProfessional certification / Application security
Application security, secure development, and testing practices.
Certified in Cybersecurity (CC)
ISC2Professional certification / General security
Foundational security principles and cybersecurity practices.
Penetration Testing, Incident Response and Forensics
IBMProfessional course / Incident response
Penetration-testing methodologies and incident response.
Crash Course on Python
GoogleTechnical course / Programming
Python programming fundamentals for automation and security scripting.
Cyber Threat Intelligence 101
ArcXSpecialized course / Threat intelligence
Threat-intelligence gathering, analysis, and application.
Masters in Cyber Forensics and Information Security
Advanced studies in digital forensics, incident response, and information-security management.
Bachelors in Computer Application (BCA)
Application development, computer-science fundamentals, and systems.
Best outgoing student for overall performance, 2020.
Get in touch.
Open to cybersecurity opportunities, consulting projects, penetration-testing projects, security research collaboration, and speaking engagements.
Languages: English, Tamil, Hindi, Malayalam, Japanese.